JCE Editor - Security concerns - Update is needed (!) - Forum | JoomShaper
Staff replied General

JCE Editor - Security concerns - Update is needed (!)

Asked by Paul Frankowski 3 months ago Last activity 3 months ago

Yes, I realize that the JCE editor isn’t ours, but I see every day that a lot of people use it. The problem is that you (webmasters) often forget to update it. And over the past few days, several vulnerabilities that hackers could exploit have been discovered in it. Fortunately, the latest version fixes these known issues. But the number of attacks labeled “Attempted to leverage vulnerability in old version of JCE” will grow every day.

Please check and update to JCE 2.9.99.6 (Core/Pro) ASAP
14 replies

Paul Frankowski Senior Staff
3 months ago · edited

If you have not updated JCE so far, please do so immediately. The vulnerability is being actively exploited, working exploit code is public, and the attacks are automated, so a site with no public registration is not safe.

Notice! JCE updating closes the entry point but does not clean a site that was already compromised. If you were hit before updating, the update will not remove what the attacker left behind.

Official note: https://www.joomlacontenteditor.net/news


Looking at my private sites, I also noticed:

  • Attempted to leverage vulnerability in old version of Novarain Framework (below v6.0.37)
  • Attempted to leverage vulnerability in old version of Opening Hours module (below v6.1.0)
ssnobben

yes good to announce things like this Paul.

Rvdzande

Also consider a manual update. I've had many sites which were 'up-to-date' but still had an old version because the update mechanism didn't see / get the newer versions. So it was shown as up-to-date.

Paul Frankowski Senior Staff

Yes, I also noticed that JCE doesn't display notes about new versions in Joomla Admin as regularly as other extensions. That's why: download JCE and reinstall on every single site that you have it.

Update JCE today, not tomorrow!

Paul Frankowski Senior Staff
3 months ago · edited

@Gregory

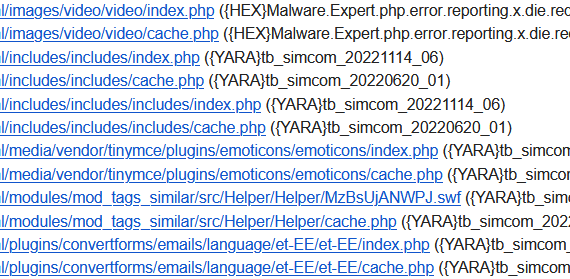
Remember to scan whole site, most "hackers" could upload over 20-30 extra malware files after success. Many of them (but not all!) are visible as new folders in the root. Some hidden files can be also inside core structure "/includes/". Real Example:

info__236.png

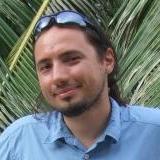
Example requests / IPs

info__rs.png

Gregory Belaus

I got sorted, but it was a lot of work. Gemini was useful for looking at what might have been touched. @Paul, yes there were many places. Luckily there was nothing destructive. If anyone else get's hacked, I can help with a list of things to look for. Thx

Paul Frankowski Senior Staff

Today, I saw two other websites damaged by JCE hole, so I guess there are many more.

Fixing it - seems to be easy, but it's always better to do more then just cleaning & updating.

Rvdzande

What I have seen that (mentioned by mysites.guru) a site is also shown in their scan as hacked, while I cannot find the hacked files.

Another site has an up-to-date version of JCE but keeps getting hacked (only two files got uploaded). Fortunately it is a test site.

Paul Frankowski Senior Staff

It’s also a matter of hosting; if the accounts aren’t segregated, if a hacker gains access to one, they can jump to another account. Plus, you need a really good malware scanner to find infected or new backdoor files. On top of that, you have to search the directory structure manually.

Log in to reply.