New Critical Security Update For SP Page Builder Pro
jcalvert
I just found out that there is another critical security update for SP Page Builder Pro, which is 6.7.1.
It's difficult to find the changelog for the software, which is here:
https://www.joomshaper.com/downloads/extension/sp-page-builder-pro-next
The changelog doesn't indicate that it's a critical security update.
And, I never got an email to warn me of this necessary update.
It seems other people are getting these emails, but I am not. Please sign me up. Please also indicate if I need to whitelist the sender. What is the sending email address?
thank you, JC
Paul Frankowski
Accepted AnswerHi,
- All users have gotten the newsletter, it was sent in 6.7.1 premiere day (27 July 2026), 2 weeks ago.
- Not really. Easy to remember, it's before Download button : https://www.joomshaper.com/downloads/extension
- It wasn't (it was hardening), previus version was.
- Check SPAM folder. It all depends on you mail-box settings. Add our e-mail to your safelist.
- You need system that will update your extensions without checking manually, there are solutions for Joomla's already, as component or online service.
And before you will write "I wasn't informed etc" in next days or week ..... the upcoming update
SP Page Builder v6.8.0 Changelog
- Update: Added a Joomla 3 version guard to the installer script. (to stops J!3 users from trying)
- Update: Hardened input validation, file handling, and access checks across the component.
- MORE
You're welcome.
jcalvert
Accepted AnswerHi Paul,
Sorry, I was relying on the AI, and the AI said... critical security update... SQL injections. It mentioned a CVE. You are saying it wasn't a critical update... OK, that's a relief. Would you call it a non-critical security update? Is v6.8.0 what you consider a security update?
I am just looking for a solid way to know when you guys have a security update for Page Builder or Helix. The June wave was traumatizing for me. No, I don't want to pay for mysites.guru. I'll look into the automatic features built into Joomla.
I'm fine if you want to change the title on the post, if you can.
I have whitelisted joomshaper.com incoming email.
Please confirm that my email address (see below) is on your email list for updates like this, and that the notifications come from @joomshaper.com.
Thanks for making these updates.
JC
Paul Frankowski
Accepted AnswerSorry, I was relying on the AI, and the AI said... critical security update.
About facts from last days, but AI is Now Faking even Critical CVEs : https://www.youtube.com/shorts/uHK-HBTJMfM
I suggest to use every update. Also becuase it fixes small issues and add new features. The same as you do for your browser.
There is also free component that have auto-update for Joomla. (info & link below)
I guess, it's not possible to change forum post title( :/ ), only content inside or delete whole topic, if you got all the answers.
I checked, and your correct e-mail is already in our system. Thanks.
djumla
Accepted AnswerHi,
David here, teamlead of the Joomla Security Team.
I'm following up with you for a couple of weeks now regarding the unpatched SQL injection, getting any sort of meaningful feedback from you guys has been "difficult" - and now you end up publicly posting about activly expoited security issues without a patch being available?
With all due respect: could you please bring your team up to speed in terms of basic security industry standards (how to handle a security issue, what does "responsible disclosure" mean, communication best practices with end users and reporters), provide feedback regarding the open issues asap and most importantly ship that damn release for an actively exploited issue.
Pascal - HTProtect.org
Accepted Answer
abrac Büro & Grafikservice Andrea Brandt
Accepted AnswerHi, Klaus from Germany here, long time Coústomer. After all that shit in the last month' i bought mysitesguru for all my sites...
And he wrote on every site this (today, August 10, 2026): ////-> in hidden content, just Paul aked, O.K.///
Paul Frankowski
Accepted AnswerOur update is planned for this week (tomorrow probably). But it will include more than only that change.
@Pascal, we both agree that using firewall is MUST HAVE, no matter what extensions you use.
@David, I agree, I removed info from my post, but @Klaus have to do the same! !!! bitte !!! Cut & paste your content in "Hidden Content" area (!) For security reasons !!
djumla
Accepted Answer@David, I agree, I removed info from my post, but Klaus have to do the same! !!! bitte !!!
Well, that underlines my point I guess: As mentioned a couple of times now, the SQLi vector is not reported through responsible discloure procedures but is actively exploited in currently running campaigns. The information about the issue is therefore already public. The real key problem is that there is no patch.
Other reported potential issues are still under responsible disclosure, but due to lack of feedback from your end I have no idea if those issues are indeed valid and when they will be adressed.
abrac Büro & Grafikservice Andrea Brandt
Accepted AnswerO.K., Paul, I did. Sorry, but I feel a bit ...insecure.
Paul Frankowski
Accepted AnswerDanke. As we all know, danger times in EU, cyber crimes on the net, mailbox full of spam, AI takes our jobs, "engineers and doctors" on the streets, extreme heatwaves and RU drones in the air. I feel the same.
djumla
Accepted AnswerFor those questions use e-mail
Well, I am using e-mail for weeks, but getting proper answers is... challening.
So, I would suggest you do these three things:
- publish the patch for the SQLi - and not tomorrow or until the end of the week, but today
- get an overview of the other pending reports by myself and the reporters that have cc'ed me
- act according to esablished best practices - and in order to make your life a little easier, I've prepared a guide: https://manual.joomla.org/docs/next/building-extensions/security/
Ping me if you have any further questions

Hans Blaettler
Accepted AnswerTo add to this discussion, just to share: RSJoomla has just released version 3.3.17 of the RSFirewall, added - Protection against SP Page Builder 6.7.1 vulnerability (changelog)
David Forés
Accepted AnswerI suppose the lack of a quick response has to do with that habit of bundling other fixes and improvements into the same release.
I’ve said it more than once: a security update should have its own release and be published immediately once it’s been tested—not wait until the other 47 updates are all properly integrated and none of them break anything.
I really don’t get it… and as I said, I’ve reported this more than once in recent weeks.
Torsten.S
Accepted AnswerAs I mentioned before, the entire Page Builder software needs a serious review.
Paul Frankowski
Accepted AnswerI will tell this way. Even your browser and OS (Windows 11 etc) still gets security updates, it's a never-ending story.
Torsten.S
Accepted AnswerWell, sure.
But for someone who is with Linux since 1998, wrong comment.
But let me put it so:
Your handling is like Windows, but we needed Linux handling instead.
But at least this got one good thing (for me).
After ages not wanting to put any effort in template building, the pagebuilder issue forced me to do so. So i will never need anything like pagebuilder again.
jcalvert
Accepted AnswerHello Paul,
When can we expect Page Builder Pro v6.8.0?
I third the motion... release the security fix now, have another release for the other fixes.
When you release v6.8.0, please post that info here on the thread. I have been getting all of the emails for this thread, but I have yet to confirm being able to receive your announcement emails.
In the mean time, should we use patch that Klaus mentioned?
One more thing... what can we look for in the Joomla database to see if a bot has made this injection?
thanks, JC
Paul Frankowski
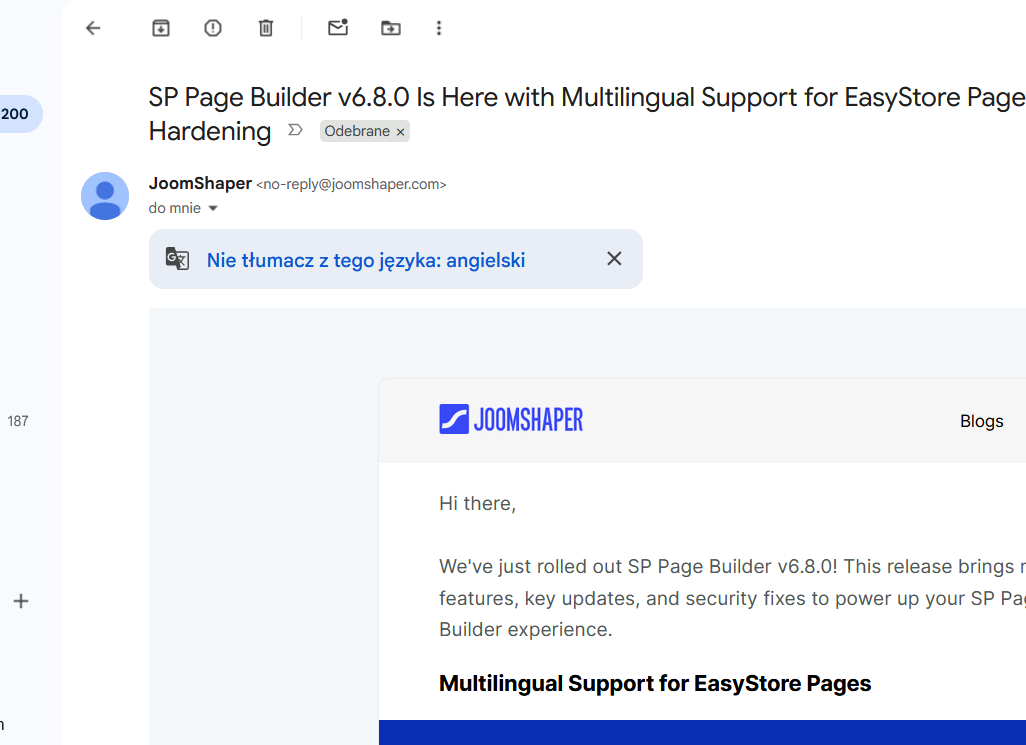
Accepted AnswerFile was published 1h ago. I hope you got the newsletter this time, it was sent in 4 sessions.
Rvdzande
Accepted AnswerOne remark about the newsletter; the security update should be the main topic.
jcalvert
Accepted AnswerHi Paul,
I did not get the newsletter, but I did get the forum notifications.
I checked my mail server log... no email from @joomshaper.com was blocked. I have that whitelisted.
It seems my address is not on your newsletter email list. (address copied in the hidden section)
MiBa
Accepted AnswerTemplates and quickstart packages should also be updated. SPPB 6.6.2, ES 2.0.1, and Helix 2.6.6 – all security holes bundled in one package for newcomers.
Kieron
Accepted AnswerI appreciate its a lot of work ... but I have NEVER had an email and Ive been with Joomshaper for 10 years! This is only going to get worse and I'm currently uninstalling all components (as much as possible) from outside official Joomla ! AI has destroyed it all!
djumla
Accepted AnswerAI has destroyed absolutely nothing. We are talking about issues in existing codebases. They are there, they are everywhere and AI only does a more or less solid job in finding them.
It's now up to the extension devs to do homework that they should have done ages ago: clean up their code bases, review their stuff, implement secure coding standards and adapt proper policies.
Addington
Accepted AnswerThe upside for developers is that they have AI too now, if they choose to use it. They can do what the hackers do: show AI the static code and ask if it to find the vulnerabilities. Then they can diverge from the hackers by fixing the code and the architecture.
It does of course mean fewer new features for a while, but that's not a problem. I used to choose extensions based on features, support and cost. From now on, its going to be security and robustness first.
We are in a new era and anyone who doesn't make that transition, is going to feel the pain.
Kieron
Accepted Answer@ djumla "AI has destroyed absolutely nothing. " ... It has destroyed my serenity! While I appreciate your arguements on AI vs AI, I was hoping for a rather slower human vs humanoid evolution. This has been very abrupt and is why software developers are struggling to keep pace. I'm in my twilight years so while its a costly pain, I'll get through it.** Love Joomla!
jcalvert
Accepted Answer@ dumla "AI has destroyed absolutely nothing. We are talking about issues in existing codebases. They are there, they are everywhere and AI only does a more or less solid job in finding them. // It's now up to the extension devs to do homework that they should have done ages ago: clean up their code bases, review their stuff, implement secure coding standards and adapt proper policies."
Yes!
@ Addington "The upside for developers is that they have AI too now, if they choose to use it. They can do what the hackers do: show AI the static code and ask [it] to find the vulnerabilities."
Yes!
For now I'll stick with Page Builder & Helix for my several sites that use it, but if I sense that the devs are not: 1) improving security update notifications, and 2) going all out to clean up their code base, then at some point I may be forced to abandon the code and use different solutions.